During this edition of the Advanced In-The Wild Malware Test, a growing trend of ransomware malware and Trojans stealing user credentials has been revealed. Appearing more often than usual ransomware samples in the wild are also confirmed by independent statistics from Check Point – experts show a significant increase in the spread of ransomware in Poland. Here is one example of LockBit 2.0 ransomware spotted in our tests:
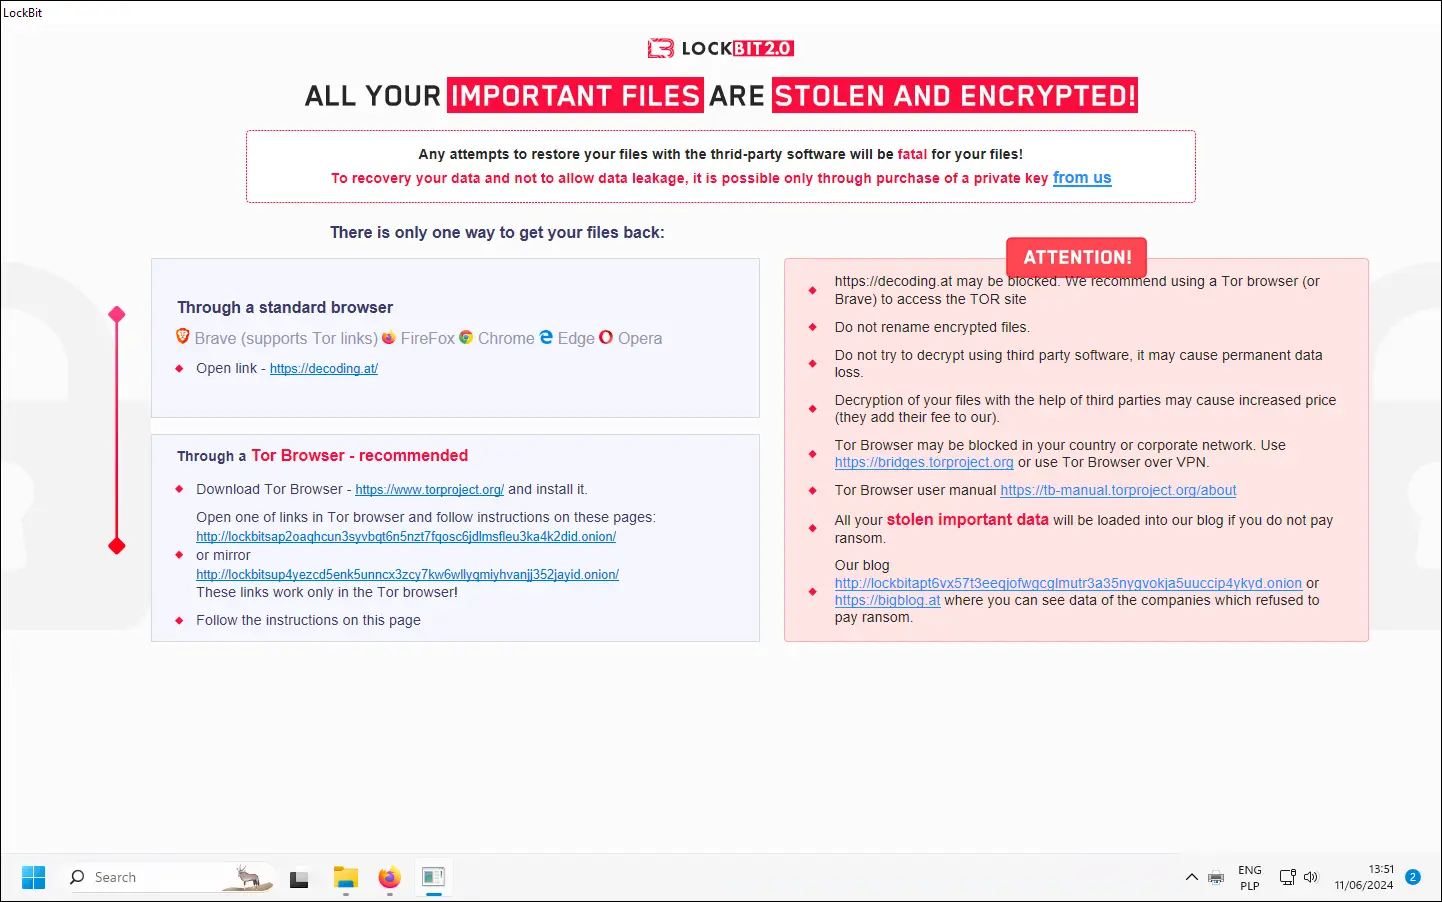
URI: 34[.] 170[.] 129[.] 13
In May 2024, we obtained a total of a dozen unique ransomware samples out of 521 of all malware samples that were qualified for the test. Let us remind that potential malware is obtained from messengers, websites, honeypots.
Our tests comply with the guidelines of the Anti-Malware Testing Standards Organization. Details about the test are available at this website as well as in our methodology.
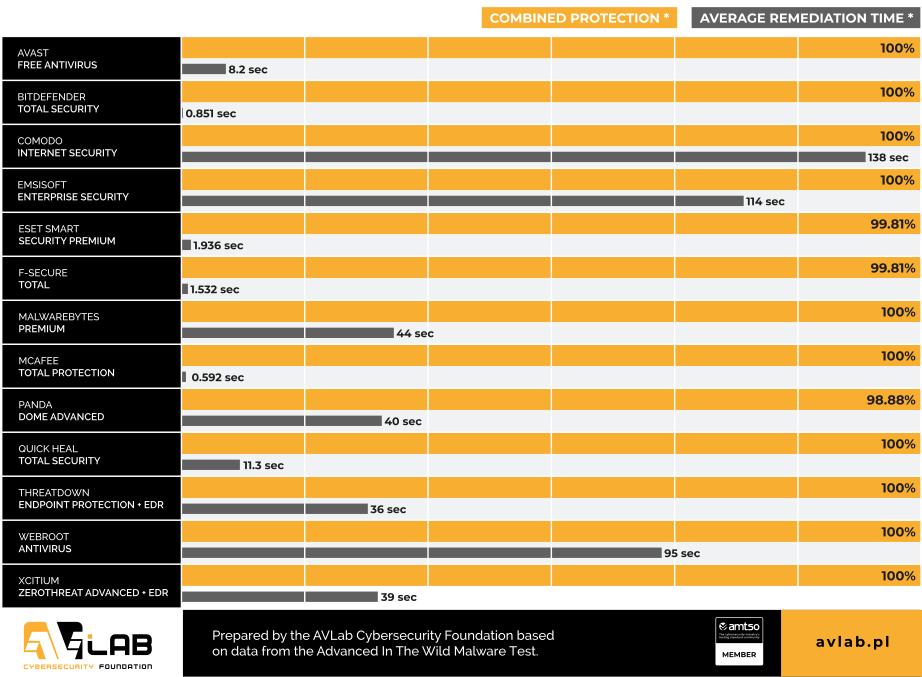
Summary of tests in May 2024
We tested 13 solutions. Almost all of them were characterized by 100% neutralization of in-the-wild threats. Almost, because Eset Smart Security software, F-Secure Total, and Panda Dome failed in one or more cases. Not all developers have managed to go through this edition flawlessly.
It is worth paying attention to the Remediation Time parameter – this is the average time of complete neutralization of a given threat from the introduction of file into the system, till blocking or neutralization of malware after being launched by the antivirus product.
Detailed results can be found on the Recent Results webpage.
The following developers have coped with the fastest neutralization and flawless removal of threats:
- McAfee (on a set of samples used, it took 0.589 seconds on average)
- Bitdefender (0.847 seconds on average)
- F-Secure (1,530 seconds on average)
- Eset (1,933 seconds on average)
- Avast (8.25 seconds on average)
Although we avoid using PUP.PUA samples in the test, it is always worth activating such a protection, and we also use these settings.
Presets are good, but not always the best. Therefore, for full transparency, we list those that we have introduced for better protection, or if it is required by a developer.
In addition to the changes below, we always configure a solution in such a way that it has a dedicated extension for the Firefox browser which we use in the tests (if the extension is available). Apart from that, we adjust the software to automatically block, delete, and recover from incidents.
The software configuration is as follows:
- Avast Free Antivirus: default settings + automatic PUP repair + browser protection.
- Bitdefender Total Security: default settings + crypto miner detection + browser protection.
- Eset Smart Security Premium: default settings + browser protection +
- LiveGrid enabled.
- PUA detection enabled.
- LiveGuard set to “end process and clean”.
- Protection and detection at the “balanced” level.
- F-Secure Total: default settings + browser protection.
- Comodo Internet Security Pro: default settings.
- Emsisoft Enterprise Security: default settings + automatic PUP repair + EDR + Rollback + browser protection.
- Malwarebytes Premium: default settings + browser protection.
- McAfee Total Protection: default settings + browser protection.
- ThreatDown Endpoint Protection: default settings + EDR + browser protection.
- Webroot Antivirus: default settings + browser protection.
- Xcitium ZeroThreat Advanced: predefined policy -> Windows Secure Profile 8.1 + EDR.
